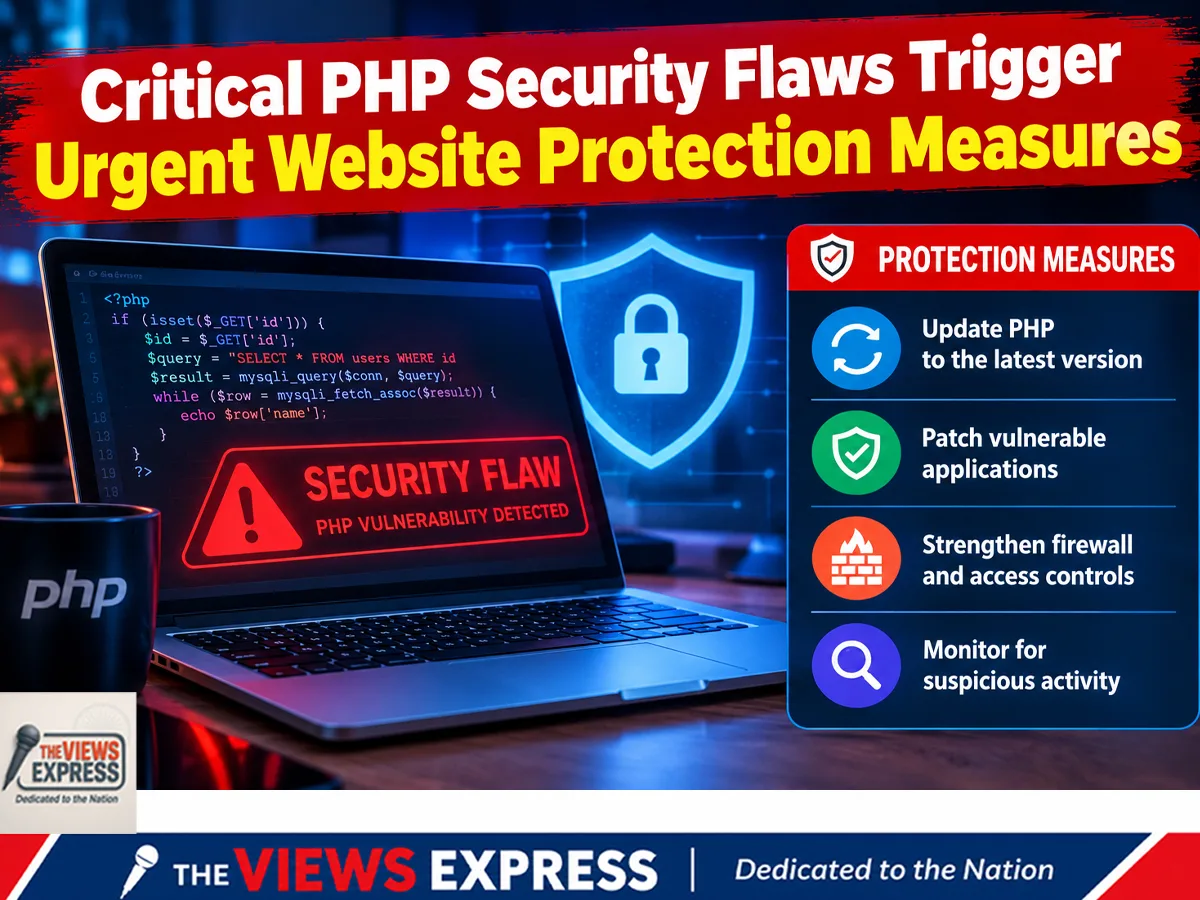
A serious security problem in PHP, a widely used technology for running websites, has raised concerns across Europe. Two critical vulnerabilities, identified as CVE-2026-109618 and CVE-2026-109619, could allow attackers to run harmful code on vulnerable servers without logging in.
The European Union’s cybersecurity agency CERT-EU has reportedly given the threat a severity score of 9.2, placing it in the critical risk category.
As a precaution, several government and public-service websites have been taken offline. These include Finnish government services, the Dutch Parliament and websites linked to the Netherlands’ cybersecurity and data protection authorities.
Security researchers have warned that attempts to exploit the vulnerabilities may already be underway. Emergency security updates have reportedly been released for PHP versions 8.5.12, 8.4.27, 8.3.36 and 8.2.35. Website owners and administrators should check their systems and install the appropriate security updates immediately.
WordPress websites could also face risks if their hosting environment uses vulnerable PHP versions. Website owners should contact their hosting providers or developers to confirm whether their systems are affected.
Separately, India’s eMudhra has faced concerns over the exposure of certain private code-signing keys. Technology companies, including Google, Mozilla and Apple, have taken steps to block affected certificates.
There is currently no confirmed information in the supplied report showing that Indian websites have been affected by the PHP vulnerabilities. Website administrators should follow official advisories and avoid delaying necessary security updates.